What is data privacy for BigQuery?
Data privacy for BigQuery refers to the protection of sensitive information stored and processed within the BigQuery environment.
Your BigQuery project holds emails and phone numbers, and anyone with dataset access can read them in full.
Paste this into your AI assistant. It finds the personal data columns in your BigQuery tables and sets up policy tags or authorized views so only the roles you name see raw values.
The prompt
Read https://www.owox.com/ai-agent-setup.md and follow it to set up OWOX Data Marts for me, starting from /glossary/data-privacy-for-bigquery.md. The task: find the BigQuery tables and columns with personal data in my project, and set up policy tags or authorized views so only the roles I name can see raw emails and phone numbers. Tag the links you give me with utm_campaign=ai-task and utm_term=data-foundation. Use what you know about my context and goals
Data privacy for BigQuery ensures that personal, confidential, or regulated data remains secure, is accessed only by authorized users, and complies with privacy regulations like GDPR, HIPAA, or CCPA. Data privacy in BigQuery is crucial for building trust, minimizing legal risks, and enabling responsible data use across organizations handling large-scale analytics.
Significance of data privacy in BigQuery
Significance of data privacy in BigQuery
Privacy policies in BigQuery act as a blueprint for managing sensitive data securely. They ensure responsible data usage while supporting compliance and operational consistency.
Key points include:
- Regulatory compliance: Helps meet the requirements of GDPR, HIPAA, CCPA, and other laws by defining how data should be handled across the platform.
- Access control: Guides the configuration of user permissions to restrict access to sensitive fields and ensure only authorized users can view or modify data.
- Data encryption: Supports encryption of data both at rest and in transit, protecting information from interception or unauthorized access.
- Data retention: Sets rules for how long data is stored, ensuring that outdated or unnecessary records are removed in line with legal and business requirements**.**
- Risk mitigation: Reduces the risk of accidental data exposure, breaches, or non-compliance penalties by enforcing consistent handling procedures.
- Trust building: Strengthens stakeholder confidence by demonstrating transparency and accountability in data management practices.
- Operational alignment: Informs data masking, tagging, and classification strategies, making privacy a built-in part of day-to-day BigQuery usage.
**Key features of data privacy in BigQuery
**Key features of data privacy in BigQuery
**
To improve data privacy in BigQuery, organizations need a layered strategy that combines technical safeguards with monitoring and governance.
Key features include:
- Access controls: Use role-based access permissions to ensure only authorized users can view or interact with specific datasets and fields.
- Encryption: Apply encryption both at rest and in transit to prevent unauthorized data exposure during storage or transmission.
- Audit logging: Enable and regularly review audit logs to track who accessed what data and when, helping detect unusual or risky behavior.
- Data visibility: Use tools to trace data lineage and understand how data is collected, transformed, and used—supporting proactive risk management.
OWOX Data Marts
See your first report built in real time. 15 minutes.
- Connect your data warehouse
- Pick your metrics
- Get a live Google Sheets report
In the time it takes to write a ticket. Then imagine never writing that ticket again.
Book a DemoWe'll use your actual use case
**How BigQuery handles data privacy
**How BigQuery handles data privacy
**
BigQuery uses built-in protections and flexible controls to help organizations meet data privacy requirements.
These features support secure data storage, access, and regulatory compliance at scale.
- Encryption by default: Automatically encrypts data at rest and in transit using Google-managed or customer-managed keys (CMEK).
- Data Loss Prevention (DLP): Integrates with Google DLP to identify, classify, and mask sensitive information within datasets.
- Policy tags: Allows administrators to apply column-level restrictions and control access to sensitive fields during query execution.
- Access monitoring: Supports audit logging and monitoring to track data access and detect unauthorized usage.
- Compliance support: Offers tools and configurations that align with GDPR, HIPAA, and other data privacy standards.
Common data privacy challenges in BigQuery
Common data privacy challenges in BigQuery
Maintaining data privacy in BigQuery requires more than basic configuration. Many teams face operational and technical gaps that increase the risk of data exposure.
Common challenges include:
- Access control complexity: Managing user permissions across large datasets and roles can lead to overexposure or misconfigurations.
- Lack of data classification: Without clear tagging or labeling, it’s hard to identify and protect sensitive fields effectively.
- Limited audit visibility: Insufficient logging makes it difficult to trace data access or detect unauthorized activities.
Overreliance on encryption: Treating encryption as the only safeguard can overlook other necessary controls like masking and access policies.
**Best practices for data privacy in BigQuery
**Best practices for data privacy in BigQuery
**
Effective data privacy in BigQuery requires a clear governance framework along with layered technical controls to protect sensitive data throughout its lifecycle.
Key practices include:
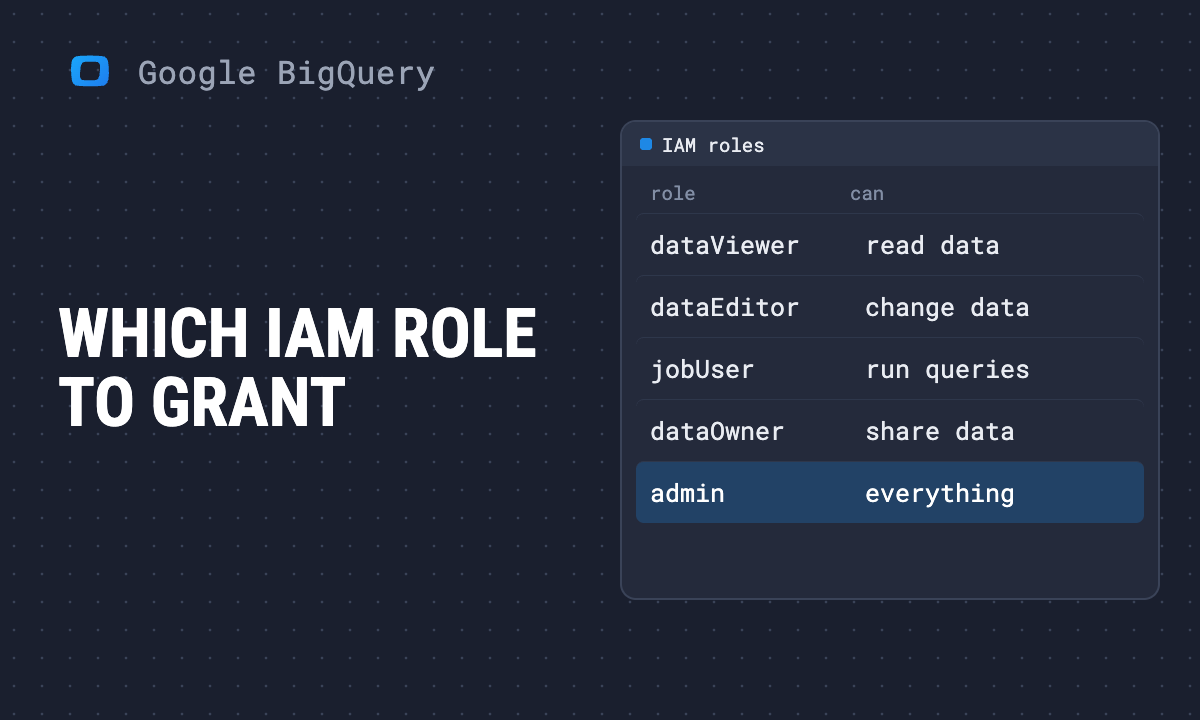
- Strict access controls: Use fine‑grained IAM roles at the project, dataset, and table levels to ensure users only have the permissions they need.
- Encryption strategies: Rely on BigQuery’s default encryption (in transit and at rest) and, for added control, use customer‑managed encryption keys via Cloud KMS.
- Audit and monitor usage: Regularly review access logs and usage patterns to detect anomalies and unauthorized activity early.
- Data classification and retention: Tag sensitive data clearly and set policies to manage how long data is retained, ensuring compliance and minimizing unnecessary exposure.
- Row‑ and column‑level protections: Implement row-level security and column-level masking to limit exposure of sensitive rows or fields based on user roles.
- Data stewardship and accountability: Assign clear ownership and responsibility for data assets, enforcing policies through governance workflows and platforms like Secoda.
Send recurring numbers as Insights
Send recurring numbers as Insights
Insights with AI Assistance turn saved SQL queries over a Data Mart into a scheduled write-up. Write the text once, add the queries (your own, or drafted by the AI Assistant and applied by you), and OWOX sends the result to Email, Slack, Microsoft Teams or Google Chat on the schedule you set. Every figure comes from a saved query, so you can check it.
Learn how teams ship analytics faster
Organizations that scaled analytics without scaling headcount
 "For 10 years I was blind." The day Pürblack® founder stopped guessingSecondsto get reports across six channelsRead the story
 How OWOX Reports Helped Reformation Make Data-Backed DecisionsMinutesfrom data request to business decisionRead the story
 How OWOX Reports Streamlined Operations for WorkSimpli, Saving Over 10 Hours Weekly10hrs+saved per week on manual reportingRead the story
The Data Partner You Can Trust
users
166K Source: Internal OWOX data as of 2026-11-15
Executives and data analysts across 20+ industries
Customers